

How sudo works
sudo lets a permitted user run a command with the rights of another user, usually root. When you run it:
- The system checks the
sudoersfile to see if you are allowed. - It asks for your password.
- It runs the command with the higher rights.
Install and set up sudo
On Debian and Ubuntu:
apt install sudoOn CentOS and Fedora:
yum install sudoCheck that it works:
sudo -h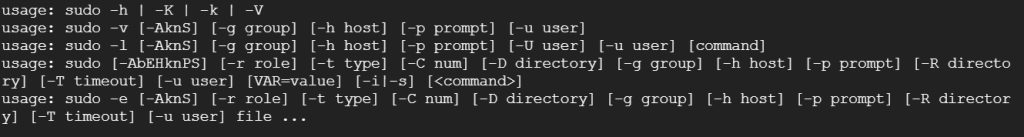
To give a user the right to use sudo, edit the sudoers file in a safe way with visudo. It checks the syntax before it saves:
sudo visudoAdd this line, with the real user name:
username ALL=(ALL:ALL) ALLYou can also add the user to the sudo group (Ubuntu and Debian) or the wheel group (CentOS):
sudo usermod -aG sudo usernameSwitch to another user
sudo su usernameTo get a full login shell as root:
sudo su - rootEnter your password when asked. You are now that user. Type exit to go back.
Log out another user
End all processes of a user:
sudo pkill -u usernameStop all processes with one name:
sudo killall process_nameChange the password of a user:
sudo passwd usernameBest practices
- Use
sudoonly when you need it. - Follow the principle of least privilege. Give users only the rights they need.
- Avoid
sudoin scripts and cron jobs when you can, because a bug runs with high rights. - Protect the
sudoersfile. Always edit it withvisudo. - Check
/var/log/auth.log(Ubuntu) or/var/log/secure(CentOS) to see who ransudo.
Quick recap
sudoruns a command with higher rights after a password check.sudo su - usernameswitches user.pkill -uends a user's processes.- Edit the rules only with
visudo.