

What is a DDoS attack?
A DDoS (Distributed Denial of Service) attack floods a server with traffic from many sources. The goal is to slow it down or take it offline. There are three main types:
- Volume attacks use up your network bandwidth with huge amounts of traffic.
- Protocol attacks abuse weak points in network protocols.
- Application-layer attacks flood one application, such as a website, with requests.
Signs of an attack
- The load on the server (CPU and memory) jumps for no reason.
- Network traffic suddenly grows.
- Visitors see slow pages or time-outs.
- A service is completely down.
Commands that help
top shows live processes and resource use.
top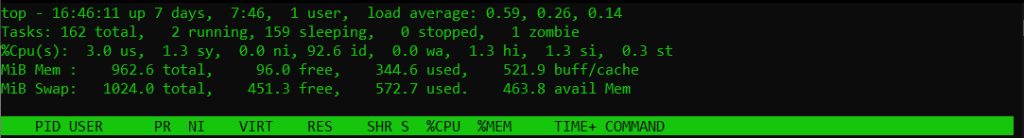
vmstat shows memory, CPU and disk activity.
vmstat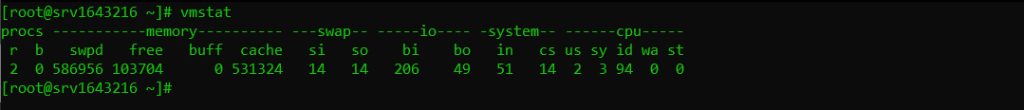
mpstat shows CPU statistics, including idle time and user and system time. It is part of the sysstat package.
mpstat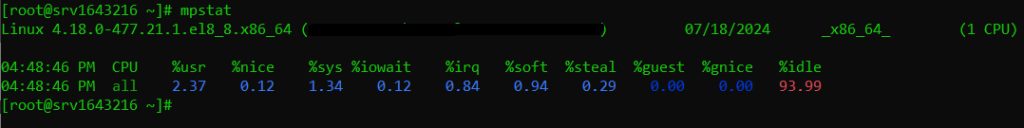
ifconfig (or ip -s link) shows network interface statistics.
ifconfignetstat shows connections and protocol statistics.
netstat -s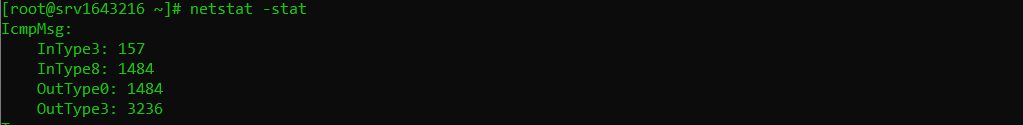
sar reports network activity at an interval. This reads the interface counters every second, five times:
sar -n DEV 1 5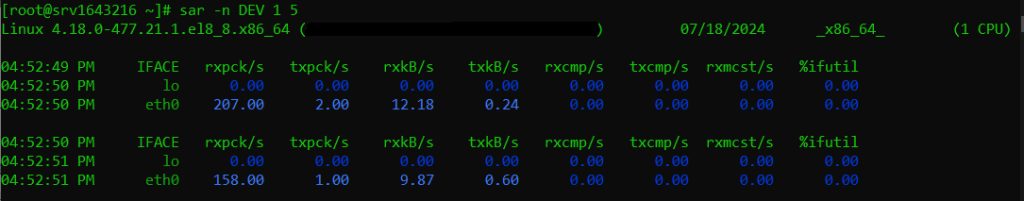
Count connections per IP address. One address with hundreds of connections is a warning sign:
netstat -ntu | awk '{print $5}' | cut -d: -f1 | sort | uniq -c | sort -n
tcpdump captures packets, so you can study them later:
tcpdump -i eth0 -s 0 -w capture.pcapYou can open the file in Wireshark, a graphical network analyzer.
What to do next
- Block abusive addresses with your firewall (for example
iptablesor UFW). - Limit connections per address and add rate limits to your web server.
- Use a service with DDoS protection or a CDN in front of the site.
- Contact Hostvento support if the attack is large. They can help you check the traffic.
Quick recap
- Look for load spikes, slow pages and many connections from one address.
- Use
top,vmstat,netstatandsarto check. - Block bad addresses and ask for help early.