

What a namespace is
A namespace is a virtual cluster inside a real cluster. It groups resources, such as pods and services, and keeps teams and projects apart. Namespaces give you:
- Isolation. Teams work without touching each other's resources.
- Quotas. You can limit what each namespace may use.
- Access control. RBAC rules can apply per namespace.
Kubernetes starts with four namespaces:
defaultfor objects with no other namespace.kube-systemfor objects made by Kubernetes itself.kube-publicwhich every user can read, even without sign-in.kube-node-leasewhich holds lease objects for node health.
Create one with kubectl
You need a running cluster. For tests, you can use Minikube on your own machine.
kubectl create namespace my-namespace
List the namespaces to check:
kubectl get namespaces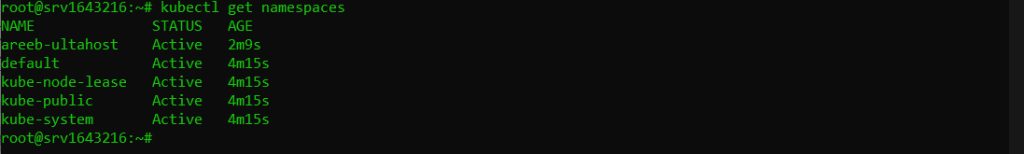
Create one with a YAML file
A file is easier to keep and share. Save this as namespace.yaml:
apiVersion: v1
kind: Namespace
metadata:
  name: my-namespace
  labels:
    name: my-namespace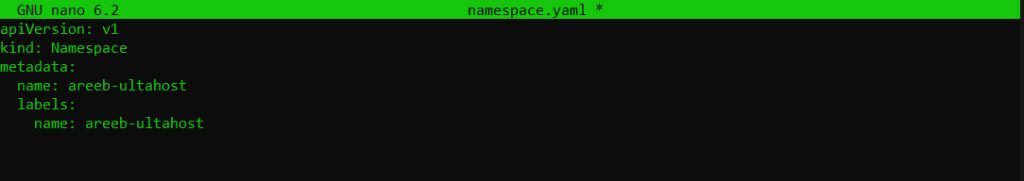
Apply it:
kubectl apply -f namespace.yaml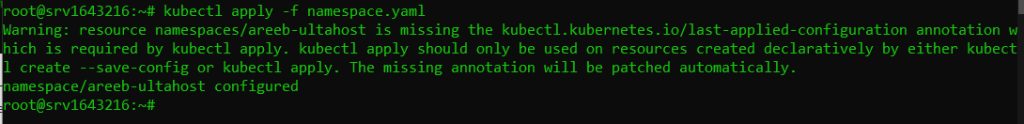
Work with namespaces
Delete a namespace (this also deletes everything inside it):
kubectl delete namespace my-namespaceUse a namespace for a command:
kubectl get pods -n my-namespaceSwitch the default namespace of your context:
kubectl config set-context --current --namespace=my-namespaceSet a resource quota. Save this as quota.yaml:
apiVersion: v1
kind: ResourceQuota
metadata:
  name: compute-quota
  namespace: my-namespace
spec:
  hard:
    requests.cpu: "2"
    requests.memory: 4Gi
    limits.cpu: "4"
    limits.memory: 8Gi
    pods: "10"
kubectl apply -f quota.yamlWarning: Deleting a namespace removes all the pods, services and data in it. Check the name twice.
Quick recap
kubectl create namespace namemakes a namespace.- Use
-n nameorset-contextto work inside it. - Add quotas to keep one project from using everything.